Preventing Data Breaches: Essential Tips for Data Security
Information Security Certification UK — preventing data breaches with ISO 27001 and AI governance
Data breaches are rising across the UK, disrupting operations, costing money and eroding customer trust. This guide explains how ISO/IEC 27001 and emerging AI governance standards such as ISO/IEC 42001 provide pragmatic frameworks to lower breach risk, align with GDPR and NIS 2, and deliver measurable security outcomes. You’ll find clear explanations of common technical and human causes of breaches, how an Information Security Management System (ISMS) operates in everyday practice, AI-specific controls to protect models and data, and practical cyber security measures that create a layered defence. We also map key regulatory actions and give step-by-step advice for UK SMEs seeking certification — including how focused certification services can speed readiness. The language throughout is risk-focused — risk assessment, access control, encryption, incident response — with practical examples security teams can use to turn policy into prevention.
What are the common causes and impacts of data breaches for UK businesses?
A data breach usually occurs when a vulnerability is exploited or a human error exposes protected information. The consequences are measurable: direct costs, regulatory fines and damaged customer trust. Identifying root causes helps organisations prioritise the technical and organisational measures that stop repeat incidents. The numbered list below summarises the most frequent causes seen across UK SMEs and larger firms, followed by the typical business impacts so teams understand why prevention must be a priority.
Common causes of data breaches:
- Human error and misconfiguration: staff send sensitive files to the wrong recipient, leave cloud storage open, or set incorrect access permissions.
- Phishing and credential compromise: targeted emails or credential stuffing enable account takeover and data theft.
- Ransomware and malware: malicious code encrypts systems and exfiltrates backups, forcing rapid recovery choices.
- Weak identity and access management: missing MFA and over-privileged accounts allow lateral movement.
- Supply-chain and third-party compromise: vendors with weak controls introduce indirect exposure through integrations.
- Unpatched software and legacy systems: known vulnerabilities remain open because of poor patching practices.
Impacts of breaches — immediate and ongoing — include:
- Direct costs for remediation, legal support and potential regulatory fines, which can reach tens or hundreds of thousands of pounds for SMEs.
- Operational disruption that lowers productivity and revenue while leadership focuses on recovery.
- Reputational damage that drives customer churn and strains partner relationships, limiting future growth.
- Higher long-term compliance and insurance costs that raise the organisation’s baseline operating expenditure.
These outcomes are well documented: poor security practices frequently correlate with financial loss and diminished customer confidence.
Data breach incidents: cyberattacks and ineffective security practices
As banking and other services move online and across borders, many data breach incidents can be traced back to weak or inconsistent security processes. Cyberattacks don’t need physical proximity and can go undetected for long periods, leaving organisations exposed to reputational and productivity losses when incidents surface.
Defining a new composite cybersecurity rating scheme for SMEs in the UK, A Patel, 2019
Which human errors and cyberattacks most often lead to breaches?
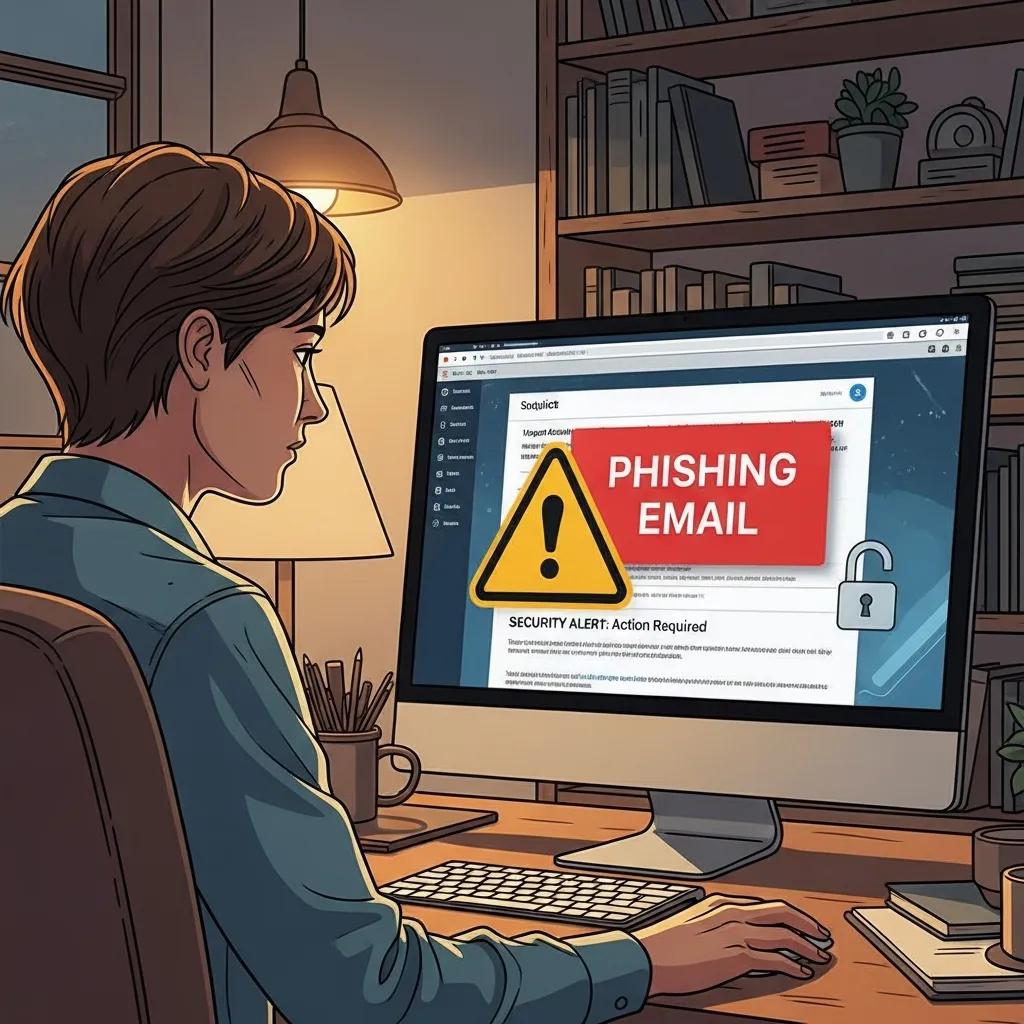
Human mistakes and common attack vectors account for the majority of incidents; addressing both reduces breach likelihood substantially. Phishing is the top entry method because it exploits trust: malicious emails trick people into revealing credentials or opening harmful attachments. Misdelivered documents, insecure sharing links and poor password practices create low-effort opportunities for attackers. On the attacker side, modern ransomware campaigns combine initial access, privilege escalation and data exfiltration before encryption to increase leverage. Practical mitigations include mandatory multi-factor authentication, least-privilege access, encryption for data in transit and at rest, and automated patching where feasible. These controls reduce the attack surface and make social-engineering attacks harder to exploit, while an ISMS coordinates measures across people, process and technology.
What are the financial and reputational consequences of data breaches?
Costs and reputation harm often outlast the technical recovery. Direct expenses include incident response, forensic investigation, legal fees, customer notifications and potential regulatory fines. Indirect costs include lost contracts, higher insurance premiums and work to remediate systemic security gaps. Reputational damage — lost trust, negative press and weakened partner confidence — can persist for months or years and is harder to quantify. For many SMEs, the combined impact can exceed annual margins, making prevention and prompt breach reporting both a legal and commercial priority. Mapping cost categories helps organisations focus investments on controls that reduce expected loss.
How does ISO 27001 certification strengthen cyber security management systems?
ISO/IEC 27001 defines an Information Security Management System (ISMS) that organises governance, risk assessment, controls and continual improvement to protect confidentiality, integrity and availability. The standard requires systematic risk assessment, selection of proportionate controls, clear responsibilities, monitoring, internal audits and management review — mechanisms that reduce breach likelihood and limit impact. ISO/IEC 27001 aligns technical measures like access control and encryption with organisational policies such as incident response and supplier due diligence, creating a coherent programme rather than ad hoc fixes. The sections that follow explain the ISMS lifecycle and how ISO 27001 turns risk assessment into practical treatment plans for data protection.
Before the example table, it’s useful to compare common control categories with their purpose and SME-friendly implementations.
This comparison shows ISO/IEC 27001 is more than a checklist: it’s a structured way to choose and apply controls that prevent common breach scenarios. The examples are starter measures SMEs can deploy quickly to stabilise their security posture.
What is an Information Security Management System?
An ISMS is a risk-driven framework that links assets, threats and vulnerabilities to chosen treatments, and then measures effectiveness through monitoring and audit. The lifecycle starts with asset identification, followed by threat and vulnerability analysis to build a risk register ranked by likelihood and impact. Treatment choices — avoid, transfer, mitigate or accept — are made with cost–benefit rationale and implemented as policies, technical controls and training. Monitoring uses KPIs and internal audits to spot failures and drive corrective action, while management review secures executive ownership and resources. This structured cycle helps organisations target limited security budgets at the risks that matter most to operations and customer data.
How does ISO 27001 implement risk assessment and treatment for data protection?
ISO/IEC 27001 requires a documented risk assessment process that links specific treatment plans to measured risk levels, ensuring controls address real threats to information. Organisations commonly use a risk matrix that combines likelihood and impact to produce a ranked register where high-priority items receive immediate technical and organisational measures. Treatment draws on controls from Annex A or equivalent baselines, adapted to the organisation’s context, with residual risk formally accepted by leadership. Continuous monitoring — logs, vulnerability scanning and incident metrics — checks control effectiveness and drives the PDCA (Plan–Do–Check–Act) cycle for improvement. This disciplined method converts reactive security into proactive risk management, lowering both breach probability and potential impact.
After adopting ISO 27001 mechanisms, many organisations benefit from external certification support. Stratlane Certification Ltd. provides accredited ISO/IEC 27001 certification combining experienced auditors with AI-assisted audit tools to streamline evidence collection and risk analysis. Their model uses locally deployed audit teams and named account managers to translate ISO/IEC 27001 controls into practical measures for organisations of different sizes. Stratlane also offers fixed-fee quotes based on organisation size and risk profile, helping you budget for certification. Choosing a provider that can both audit and advise on remediation speeds the journey from gap identification to certified status while keeping prevention outcomes in focus.
AI is increasingly integrated into security practices — for example, AI-assisted auditing — and is recognised for improving threat detection and response in ISO 27001-aligned environments.
AI for cyberattack prediction in ISO 27001 environments
Recent research compares AI techniques against traditional methods for forecasting cyberattack trends in ISO/IEC 27001-compliant environments. Simulated evaluations of algorithms such as neural networks, random forests, SVMs and Bayesian networks show AI approaches can improve detection accuracy and speed up incident response compared with conventional techniques.
The Role of Artificial Intelligence in Predicting Cyber Attack Patterns and Offering Solutions to Mitigate Attacks in ISMS Compliant Environments, 2024
In what ways does AI data governance certification prevent AI-related data breaches?
AI data governance certification targets risks that arise when models handle sensitive or large-scale datasets by enforcing controls for data quality, provenance, access and model security. AI-specific threats — data poisoning, prompt injection and model inversion — need governance that combines data protection with lifecycle controls, monitoring and incident handling tailored to AI systems. Certification frameworks formalise accountability, define model-owner roles and create auditable processes for data handling and model updates. The sections below outline core AI governance principles and how ISO/IEC 42001-style controls map to privacy and security to reduce the chance of AI-driven breaches.
What are the key principles of AI risk management and ethical AI compliance?
AI risk management relies on a few core principles that directly reduce breach risk: transparency, accountability, risk-based controls and ethical design. Transparency means documenting datasets, labels and key decision logic so parts of the pipeline are auditable. Accountability assigns ownership for model outcomes and data handling, ensuring someone is responsible for security and privacy decisions. Risk-based controls scale protections to data sensitivity and model criticality — for instance, stricter access and monitoring for models using personal data. Ethical design limits harmful outputs and unintended exposure through safeguards in training and inference. Together, these principles make it harder for attackers to exploit AI for data exfiltration or manipulation.
- Transparency: record datasets, preprocessing steps and decision rationale to support audits.
- Accountability: designate model owners and clear escalation routes for AI incidents.
- Risk-based controls: apply stronger protections to high-risk models and sensitive data.
- Ethical design: build safeguards to prevent misuse and limit unintended data exposure.
These principles underpin operational controls that mitigate AI-specific breach vectors.
How does ISO 42001 support AI data privacy and security controls?
ISO/IEC 42001-style certification prescribes lifecycle governance for AI that maps directly to data privacy and security controls: policies for data handling, model access restrictions and behaviour monitoring. Practical clauses address dataset provenance, consent and minimisation, and require logging and explainability measures to detect anomalous model interactions that might signal prompt injection or model inversion. Controls such as segmented training environments, strict access to training data and production monitoring reduce the attack surface and speed incident response. For SMEs, scaled versions of these controls — focused on high-risk models — can provide meaningful protection without excessive overhead. Integrating AI governance into an existing ISMS creates consistent controls across traditional IT and AI systems.
Some organisations choose to combine ISO/IEC 42001-style audits with broader security certification. Stratlane Certification Ltd. offers tailored AI governance audits and ISO/IEC 42001 certification alongside ISO/IEC 27001, using AI-enabled audit tools and experienced lead auditors to assess model risk, data handling and governance. This approach treats ISO 42001 as a practical extension of established information security programmes, helping organisations manage AI-specific risks while staying aligned with data protection obligations.
Which cyber security best practices complement certification for data breach prevention?
Certification sets governance and baseline controls, but effective breach prevention also requires day-to-day technical and people-focused practices. Employee training and incident preparedness, network and cloud hardening, endpoint protection and supply-chain diligence should operate alongside ISO frameworks to reduce residual risk and improve recovery. The list below highlights high-impact practices with concise rationales for operational planning. After the list, a technical mapping table links security areas to the specific risks and controls teams can act on immediately.
High-impact cyber security best practices:
- Employee security awareness and phishing simulation: measured training reduces successful social-engineering attacks.
- Robust incident response and tabletop exercises: these shorten detection and containment times to limit impact.
- Network segmentation and endpoint detection and response (EDR): prevent lateral movement and enable rapid containment.
- Cloud configuration hygiene and IAM controls: stop data exposure from misconfigured services and weak identities.
- Third-party risk assessments and contractual controls: close supply-chain gaps that often lead to breaches.
These practices operationalise certification controls and produce measurable metrics for continuous improvement.
This technical mapping gives teams actionable controls that align with ISO/IEC 27001 categories and should be reflected in the ISMS risk register and treatment plans. Implementing these controls reduces the attack surface and supports faster recovery when incidents occur.
How can employee security awareness and incident response reduce breach risks?
Awareness and incident response are the human and procedural layers that detect and contain incidents before they escalate. Awareness programmes should include role-based training, targeted phishing simulations with measurable metrics, and clear reporting channels so staff spot and escalate suspicious activity. Incident response needs a documented plan with defined roles, communications templates, forensic readiness and regular tabletop exercises to validate playbooks. Metrics such as time-to-detect, time-to-contain and phishing click rates measure effectiveness and feed improvements to training and controls. Together, these activities reduce successful compromises, shorten recovery windows and provide evidence for regulatory reporting and insurance claims.
What network, cloud and supply chain security measures are essential?
Technical controls across network, cloud and supply chain domains remove the common exploitation paths attackers use and provide consistent protection across assets. Network segmentation limits attacker movement between critical systems and user environments, while EDR and behavioural detection flag suspicious endpoint activity. Cloud hygiene — configuration scanning, IaC reviews and strong identity controls — prevents accidental exposure. Supply-chain security requires due diligence, contract clauses and periodic reassessment of third-party posture. Implemented with monitoring and alerting, these measures give teams the telemetry and controls they need to respond when anomalies occur.
What data protection compliance services and regulations must UK businesses follow?
UK organisations should align security programmes to core data protection laws and sector directives to lower regulatory risk and improve breach readiness. The primary regulations are GDPR and the UK Data Protection Act 2018 for personal data, and NIS 2 for operators of essential services and digital service providers. Emerging AI rules will add governance requirements where models process personal data. The table below maps regulations to immediate business actions you can take to prioritise compliance and readiness.
How do GDPR and the UK Data Protection Act influence data breach prevention?
GDPR and the UK Data Protection Act 2018 require appropriate technical and organisational measures to protect personal data, making prevention both a legal and operational priority. Practical steps include conducting Data Protection Impact Assessments for high-risk processing, enforcing strong access controls and encryption, and keeping accurate Records of Processing Activities to show accountability. The rules also require timely breach notification in specific cases, so incident response and notification playbooks are essential. Aligning ISMS processes with these obligations reduces breach likelihood and mitigates regulatory consequences if an incident occurs.
What are the implications of NIS 2 and emerging AI regulations?
NIS 2 raises expectations for cybersecurity among essential and digital service providers by requiring risk management measures, incident reporting and supply-chain oversight; organisations in scope must document security policies, perform regular risk assessments and demonstrate preparedness through audits and reporting. Emerging AI regulations — especially for high-risk applications — will likely demand transparency, model risk assessments and governance over datasets, intersecting closely with data protection duties. Preparing means integrating AI governance with ISMS processes, mapping dependencies and ensuring monitoring and reporting capabilities to meet both cyber security and regulatory scrutiny.
How can UK SMEs achieve effective data breach prevention through Stratlane’s certification services?
SMEs need pragmatic, budget-aware routes to reduce breach risk while meeting compliance obligations. Certification combined with tailored support provides a clear path. Stratlane Certification Ltd. offers SME-focused ISO services with named account managers and lead auditors to guide implementation, translating ISO/IEC 27001 and ISO/IEC 42001 controls into proportionate actions for smaller organisations. Their service uses AI-assisted auditing to speed evidence collection and analysis, and accredited certification that validates your ISMS. Stratlane runs local audit teams across jurisdictions and provides fixed-fee quotes based on organisation size and risk profile, helping SMEs plan financially for certification and surveillance.
Research highlights the importance of strong information security standards for UK SMEs, many of which have yet to adopt formal certification despite rising cyber threats.
UK SME cybersecurity: threats, standards and certification
The UK’s 5.7 million SMEs are central to the economy, yet many face growing cyber threats — surveys show around four in ten businesses experienced an attack in the last year. Implementing established information security standards is an effective treatment, but most SMEs are not yet certified even though government guidance and reporting highlight the risks.
Defining a new composite cybersecurity rating scheme for SMEs in the UK, A Patel, 2019
For practical adoption, SMEs should follow a staged roadmap that balances speed and quality:
- Carry out an initial gap assessment to identify high-risk assets and immediate controls.
- Implement priority technical controls (IAM, MFA, encryption, patching) and core policies.
- Document processes, run internal audits and remediate findings before external assessment.
- Book stage 1 and stage 2 audits with a certification body and prepare for ongoing surveillance.
This phased approach reduces exposure quickly while aligning the organisation for certification and continuous improvement.
What tailored support and SME schemes does Stratlane offer for ISO 27001?
Stratlane’s SME schemes match the scale and risk profile of smaller organisations, offering practical guidance and simplified certification routes without weakening control effectiveness. Support includes a named account manager to coordinate work and a lead auditor who gives pragmatic remediation advice suited to SME operations. Fixed-fee quotes are based on size and risk profile to provide predictable budgeting. Typical timelines start with a gap assessment, a focused implementation phase for core controls, then staged audits — helping small teams prioritise high-impact measures and demonstrate compliance with minimal disruption.
What is the certification process, costs and timeline for achieving compliance?
The certification journey typically follows a familiar sequence: gap assessment, implement required controls, internal audit and management review, then stage 1 (documentation review) and stage 2 (on-site or remote) certification audits, followed by surveillance cycles. Costs depend on complexity, but Stratlane’s fixed-fee model — determined by organisation size and assessed risk — helps SMEs forecast expenses without surprises. Timelines from initial assessment to certification often span a few months for organisations that already have basic controls; those needing significant remediation will take longer. Prioritising compensating controls such as MFA, patch management and incident playbooks shortens the path to certification and meaningfully reduces breach risk while formalising the ISMS.
Frequently asked questions
What is the role of employee training in preventing data breaches?
Employee training is vital: it gives staff the tools to spot and respond to threats. Regular, role-based sessions and simulated phishing campaigns help people recognise suspicious emails and avoid common mistakes. A culture of security awareness — reinforced by clear reporting channels — cuts the chance of human error leading to a breach and speeds incident detection when something goes wrong.
How can SMEs effectively manage third‑party risks?
Third‑party risk management is essential because vendor weaknesses can become your exposure. Conduct security assessments, review suppliers’ controls, and include clear security requirements in contracts. Use questionnaires and periodic checks, maintain open communication about incidents, and monitor critical suppliers to reduce the chance of supply‑chain-related breaches.
What are the benefits of integrating AI into information security practices?
AI enhances detection and response by analysing large datasets quickly to spot patterns and anomalies. It can automate routine tasks so security teams focus on complex investigations, and provide predictive insights that surface vulnerabilities before they’re exploited. When applied carefully, AI makes your security posture faster, more scalable and more proactive.
How does ISO 27001 certification impact an organisation’s reputation?
ISO 27001 certification signals a formal commitment to information security and data protection. It reassures customers, partners and stakeholders that you follow an internationally recognised standard, which can build trust, open business opportunities and differentiate your organisation in competitive markets.
What steps should be taken after a data breach occurs?
Follow your incident response plan: contain the breach, assess the scope, preserve evidence and notify affected parties and regulators as required. Conduct a forensic investigation to identify root causes, remediate gaps and update policies and controls based on lessons learned. Swift, structured action limits damage and helps meet legal and contractual obligations.
What are the key components of an effective incident response plan?
An effective plan defines clear roles and responsibilities, communication protocols for internal and external stakeholders, and procedures to identify, contain and eradicate threats. It should include recovery steps, post‑incident review and improvement actions. Regular testing and updates ensure the plan stays effective as threats evolve.
How can organisations ensure compliance with GDPR and other regulations?
To stay compliant, implement a data protection programme that includes DPIAs for high‑risk processing, clear data handling policies and accurate Records of Processing Activities. Ensure timely breach notification processes, train staff on data protection principles and perform regular compliance audits. These steps help demonstrate accountability and reduce regulatory risk.
Conclusion
Adopting ISO 27001 and AI governance standards materially improves data protection and reduces breach risk for UK organisations. These frameworks help you meet regulatory expectations while building a culture of security and resilience. Taking proactive steps towards certification protects sensitive information and strengthens trust with customers and partners. Begin your journey to stronger information security today by exploring our tailored certification services.