Protect Against Malware: Best Antivirus Software Solutions
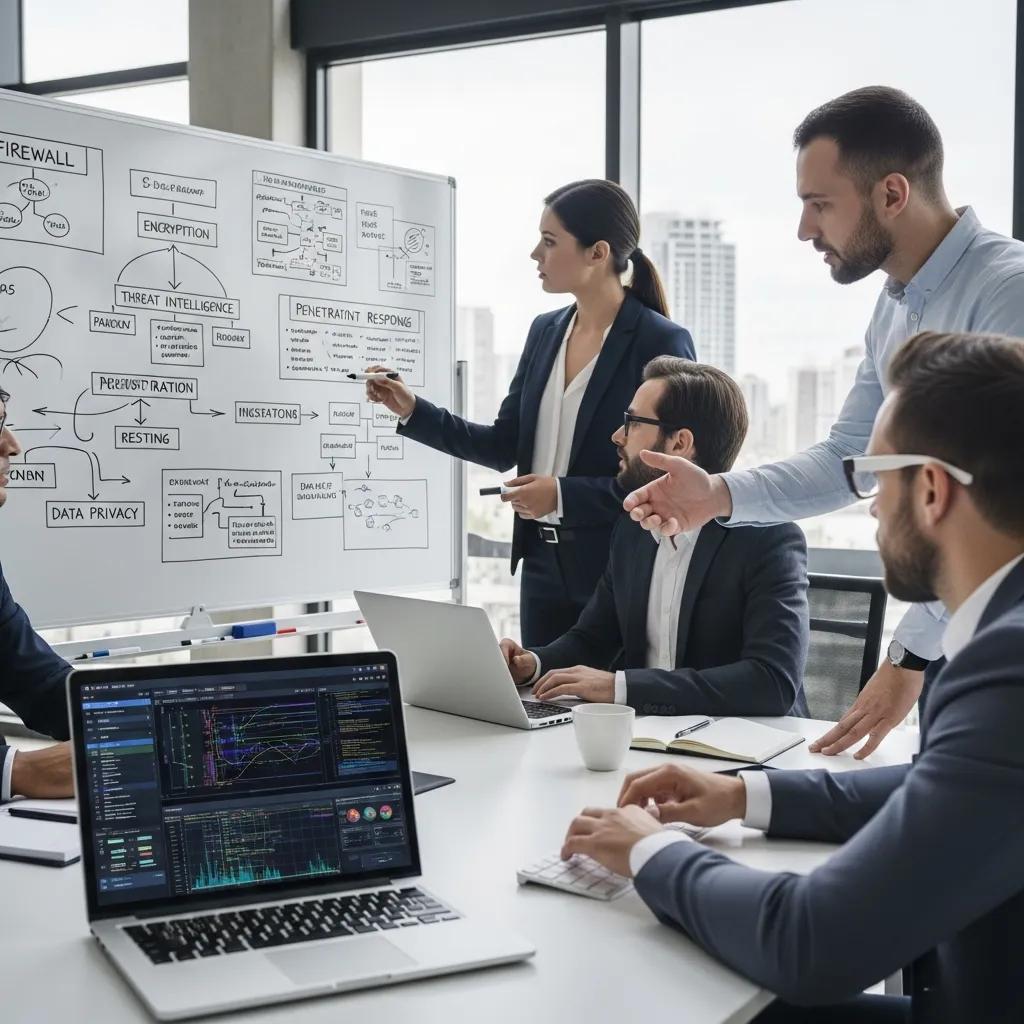
Protecting Against Malware: Business Cyber Security Solutions UK with ISO 27001 Certification
Malware — software created to disrupt, damage or gain unauthorised access to systems — is a leading source of financial loss and operational disruption for UK organisations, from small businesses to large enterprises. This guide explains how organisations can spot common malware vectors, estimate business impact, and use structured frameworks such as ISO 27001 and ISO 42001 to reduce risk, detect incidents and recover quickly. After a concise overview of threats and impacts, we map ISMS controls and practical technical measures (endpoint protection, patching, backups and training) into an actionable defence posture. We then cover AI-related malware risks and how ISO 42001 governance lowers that exposure, outline resilient backup and recovery practices, and explain how Stratlane Certification Ltd. supports organisations pursuing accredited ISO certification. Finally, we invite readers to request a quote or book an audit to begin improving resilience.
What Is Malware and How Does It Threaten UK Businesses?
Malware is software created to compromise the confidentiality, integrity or availability of digital assets by exploiting vulnerabilities, social engineering or supply-chain gaps. It can execute code, exfiltrate data, encrypt files or persist covertly, causing data loss, service outages and regulatory exposure for UK organisations. Many SMEs are particularly vulnerable: limited IT resources and extended supply chains increase attack surface and delay detection. The sections that follow describe common malware types and the practical financial and operational impacts businesses face. Understanding these categories helps organisations prioritise controls and prepare ISO 27001-aligned response playbooks.
To expand on malware’s characteristics and detection methods, research highlights the threat’s pervasiveness and the primary identification approaches in use.
Malware definition, impact and common detection approaches
Malicious software is designed to damage systems, steal information or disrupt operations without the owner’s consent. Its effects range from degraded performance to full system compromise. Researchers have developed detection techniques to protect systems, most notably signature-based methods that match known malware patterns and heuristic or behaviour-based approaches that identify suspicious activity. While signature checks are precise for known threats, heuristic and behavioural models help detect novel or modified malware, though each approach has limits and trade-offs.
Which Common Malware Types Affect Businesses?
Ransomware encrypts files or systems and demands payment, directly blocking access to crucial services and risking data loss. Trojans disguise themselves as legitimate software but deliver payloads such as remote-access tools to deepen compromise. Spyware and data-stealing malware exfiltrate credentials and intellectual property for fraud or resale, damaging confidentiality. Worms spread rapidly across networks by exploiting unpatched services, causing large-scale outages. Fileless malware runs in memory and abuses legitimate system tools to evade signature-based defences, complicating forensics. Recent trends through 2023–2024 show growing diversity in techniques and a rise in combined extortion schemes that pair data theft with encryption.
What Are the Financial and Operational Impacts of Malware Attacks?
Malware incidents carry immediate costs — forensic analysis, system restoration and specialist support — and may include ransom payments or legal fees for breach notification. Indirect losses include revenue lost during downtime, reputational damage that erodes customer trust, and potential regulatory penalties when personal data is involved. Operational consequences range from reduced productivity to supply-chain delays and higher insurance premiums. Key impact categories include:
- Direct financial loss : ransom payments, remediation and consultant fees.
- Operational downtime : hours or days of service unavailability.
- Compliance and legal costs : investigation, reporting and possible fines.
The scale of operational impact usually determines whether an organisation requires immediate incident response, extended recovery or strategic changes to security controls.
How Does ISO 27001 Information Security Protect Against Malware?
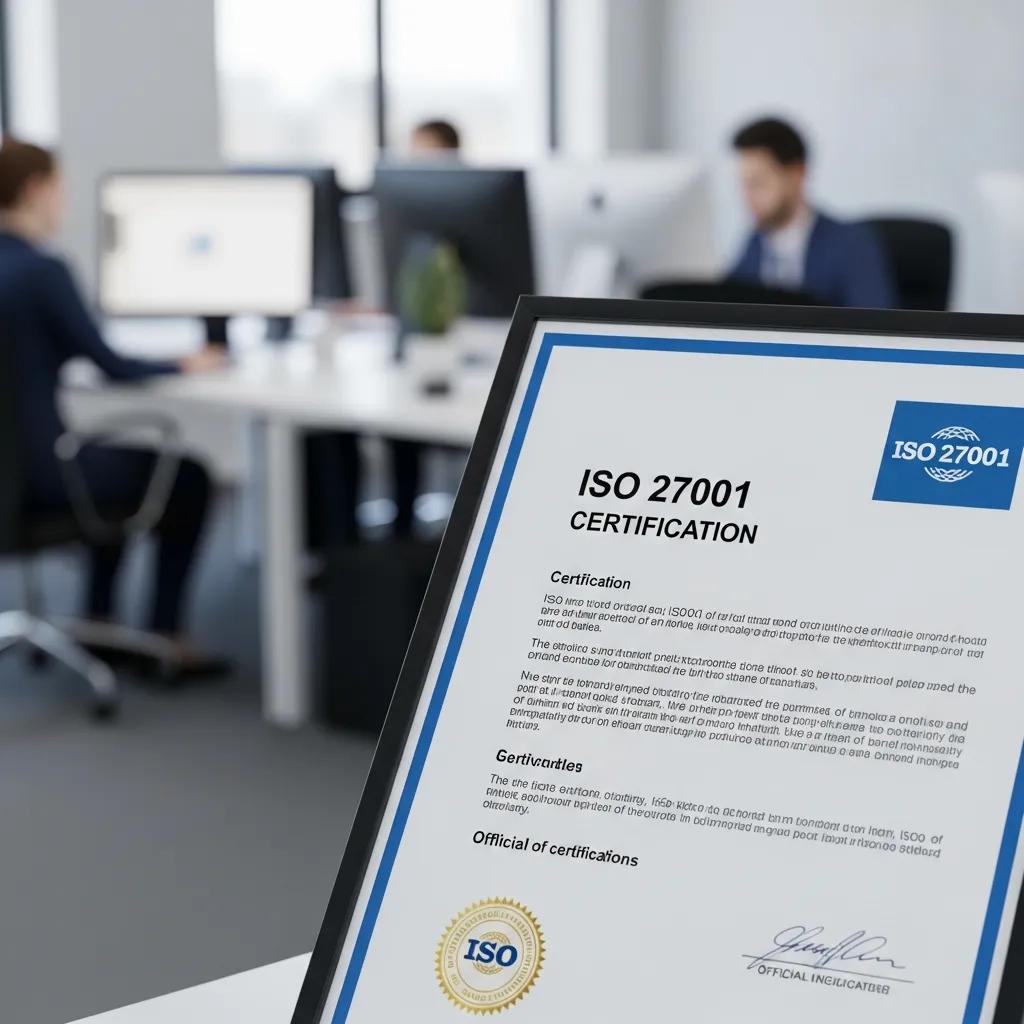
ISO 27001 establishes an Information Security Management System (ISMS) that frames risk assessment, control selection and continual improvement to reduce malware exposure and speed detection and response. The ISMS lifecycle — context, risk assessment, risk treatment, control implementation and review — creates repeatable processes that prioritise high-risk assets and link technical controls to organisational responsibilities. Implementing ISO 27001 encourages consistent patch management, least-privilege access, thorough logging and tested incident response, all of which reduce attack surface and improve forensic readiness. The sections below map Annex A controls to practical anti‑malware measures and explain how ISO processes mitigate ransomware.
What ISMS Controls Address Malware Prevention and Detection?
An ISMS ties controls to business risk so malware defences are measurable and auditable rather than ad hoc. Controls covering asset management, access control, secure configuration and operations management drive actions such as deploying AV/EDR, hardening endpoints, segmenting networks and centralising logs. Monitoring and detection are supported by event logging, continuous monitoring and vulnerability management, which together underpin early detection and effective investigation. The table below links representative ISO controls to real-world anti‑malware steps so governance translates into technical practice.
Introductory mapping of ISO controls to practical malware actions:
This mapping shows how ISO-driven controls convert policy into specific anti‑malware technologies and operational routines. Strong governance then supports continuous improvement and regular testing of those measures, which is especially important for ransomware readiness.
How Does ISO 27001 Support Ransomware Prevention for Businesses?
ISO 27001 reduces ransomware risk by requiring risk‑based treatment plans that prioritise critical systems, enforce backup strategies and mandate access controls and segregation of duties. In practice, organisations identify high‑value data, apply network segmentation to limit lateral movement, implement privileged access management and ensure backups are isolated and regularly tested.
Tabletop exercises and incident response processes required by the ISMS ensure teams rehearse ransomware scenarios and measure recovery time objectives. A simple checklist aligned to ISO practices helps businesses plan mitigation:
- Perform a focused risk assessment: identify systems with highest impact and likelihood.
- Enforce least‑privilege access and segmentation: reduce attack paths and privilege misuse.
- Implement tested, isolated backups: ensure backups are immutable or air‑gapped where possible.
- Run incident drills and forensic readiness tasks: validate communication and recovery steps.
Following these ISO‑aligned steps builds demonstrable resilience and supplies evidence for auditors and stakeholders that ransomware risk is actively managed.
What Practical Cybersecurity Measures Complement ISO 27001 Certification?
ISO 27001 provides governance, but technical and operational controls reduce dwell time and improve resilience. Practical measures include deploying modern endpoint protection, prioritising fast patching, centralising telemetry for detection and using continuous employee awareness programmes. Together these layers — policy, people and technology — form a resilient defence. The subsections below compare endpoint protection options and explain how training reduces human‑enabled infection vectors, both necessary complements to an ISMS.
Which Endpoint Security and Antivirus Solutions Are Effective for SMEs?
Endpoint protection ranges from signature‑based antivirus to cloud native Endpoint Protection Platforms (EPP) and Endpoint Detection and Response (EDR) systems that combine prevention with behavioural detection. For SMEs, managed antivirus services offer baseline protection with predictable costs, while EPP/EDR delivers advanced detection at greater complexity and cost. The table below compares options by SME suitability, cost and management overhead to support procurement decisions.
Recent research highlights the particular challenges smaller organisations face on mobile and endpoint security, underlining the need for pragmatic protection strategies.
Mobile security framework for SMEs: malware and endpoint protection
Mobile devices improve flexibility and productivity, but they also add attack surface: malware, phishing, data leakage, network attacks, malicious apps, insider risk and risks from jailbroken or rooted devices. Managing these risks is critical for enterprises and SMEs alike. The study proposes a practical framework to strengthen mobile security posture by combining Mobile Application Management (MAM), endpoint protection and SIEM capabilities to improve detection and control.
This comparison highlights trade‑offs: managed services reduce in‑house burden, EDR gives deeper visibility and cloud EPP balances capability with ease of use. Choose based on risk appetite and ISO‑defined priorities.
How Can Employee Cybersecurity Training Reduce Malware Risks?
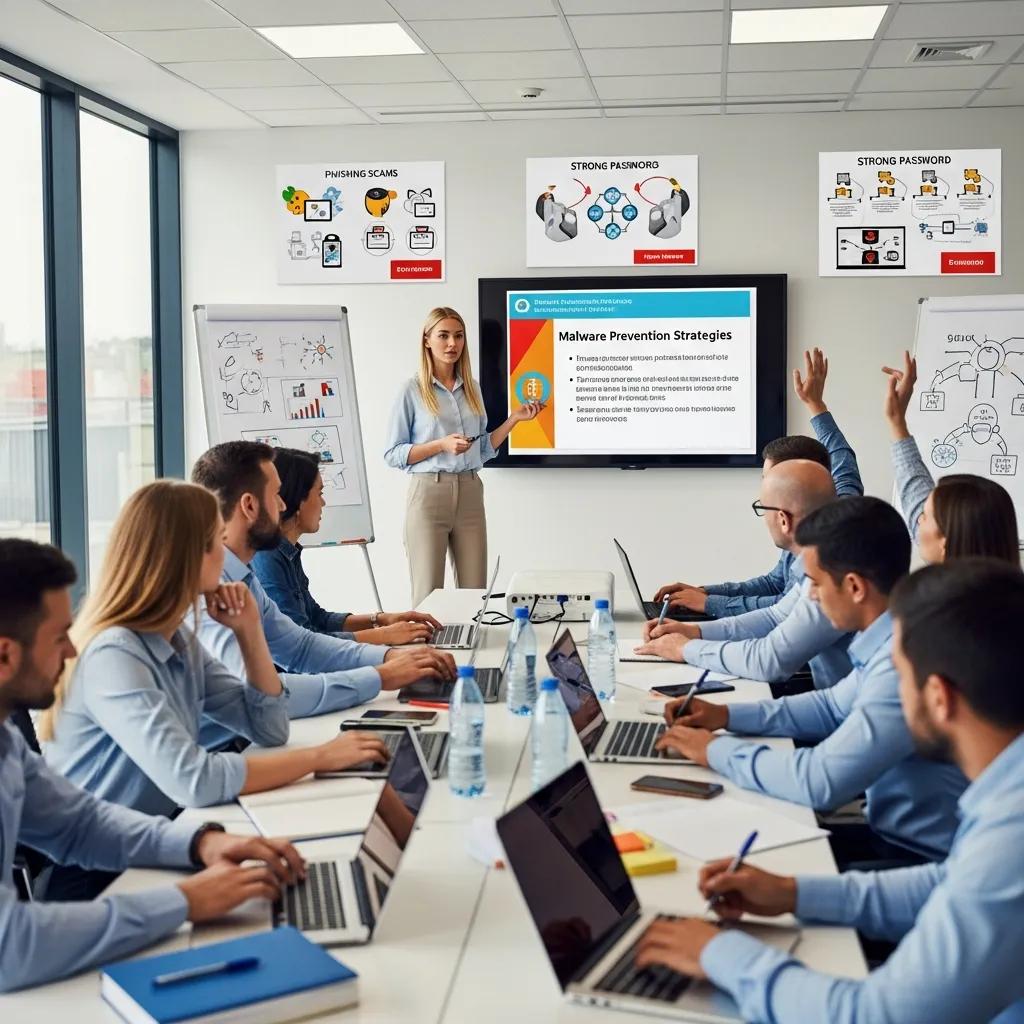
Human error is a primary malware vector — phishing links, malicious attachments and unsafe removable media. Targeted training reduces click rates and speeds incident reporting. Effective programmes combine role‑based modules, simulated phishing campaigns and regular refreshers, with KPIs such as reduced click rates and increased reporting to track progress. We recommend quarterly simulated exercises with monthly micro‑learning to reinforce secure behaviours and meet ISO awareness expectations. Use simulation results to refine content and feed findings back into the ISMS risk assessment.
- Training types to include: phishing simulations, role‑specific secure practices and executive briefings.
- Key KPIs : phishing click rate, training completion and incident report frequency.
- Continuous improvement: use simulation data to target retraining and update technical controls.
Routine training embeds a security culture and reduces the chance that malware reaches critical systems, complementing technical defences and ISO processes.
How Does ISO 42001 Address AI-Specific Malware Threats?
AI systems introduce new threat vectors such as adversarial manipulation, data poisoning and model exfiltration that can degrade decisions or expose sensitive training data. ISO 42001 sets out an AI Management System (AIMS) framework that aligns governance, lifecycle controls and monitoring to reduce these risks. By defining requirements for dataset integrity, model validation and continuous monitoring, AIMS helps ensure model provenance and operational safeguards. The subsections below explain AI‑specific threats and list governance measures ISO 42001 encourages to protect model integrity.
What Are AI Malware Threats and Their Business Implications?
Adversarial attacks craft inputs to cause misclassification or failure, while data poisoning corrupts training datasets to bias models or introduce backdoors. Model theft or unauthorised inference exposes intellectual property and can enable fraud. These threats can undermine business decisions, customer safety and regulatory compliance where AI outputs inform critical services. Short scenarios show the impact: a poisoned training set producing faulty fraud detection can increase false positives and operational cost; adversarial inputs that mislabel results erode customer trust. Treat AI assets with the same rigour as other critical systems: apply lifecycle controls and monitoring to detect drift and manipulation.
How Does ISO 42001 Ensure Ethical and Secure AI Use?
ISO 42001 prescribes governance for the model lifecycle including data quality controls, versioning, explainability and continuous validation to spot anomalies or drift. Practical measures include secure data pipelines, controlled access to model artifacts, routine adversarial testing and audits of training data sources. An AIMS checklist for secure AI covers model provenance, adversarial robustness tests, monitoring for distributional change and documented incident response for model compromise. Implementing these controls helps organisations demonstrate responsible AI practice and reduce risks that could otherwise cause operational failure or reputational harm.
- AIMS governance items: data governance, model validation, monitoring and explainability.
- Operational practices: adversarial testing, access controls and artifact versioning.
- Compliance context: readiness for evolving regulation through embedded lifecycle controls.
Following AIMS principles keeps AI systems reliable and lowers the attack surface for AI‑specific threats.
What Are Effective Data Backup and Disaster Recovery Strategies Against Malware?
Resilient backup and recovery practices are a critical last line of defence against malware, particularly ransomware that targets primary data stores. Effective strategies combine multiple backup types, isolation (air‑gapped or immutable storage), encryption and regular verification via restore testing. Recovery Point Objectives (RPO) and Recovery Time Objectives (RTO) should be set by business criticality and validated through rehearsals to ensure recovery procedures meet operational needs. The following sections give practical steps for secure backups and guidance on realistic RPO/RTO targets for SMEs.
How Should Businesses Implement Offline and Secure Backup Solutions?
Use layered backups: local snapshots for fast restores, remote immutable copies for resilience and periodic offline or air‑gapped archives to prevent simultaneous compromise. Key steps include encrypting backups, restricting access to backup systems and automating integrity checks and restore drills. When selecting suppliers, prioritise immutability, proven recovery workflows and documented encryption in transit and at rest. Regular verification — monthly partial restores and annual full recovery exercises — ensures backups are usable and supports ISO business continuity requirements.
- Implementation steps: configure immutable storage, encrypt backups, restrict backup access and schedule regular restore tests.
- Supplier checks: confirm immutability, encryption and recovery SLAs.
- Testing frequency: monthly partial restores and at least annual comprehensive recovery exercises.
These measures make backups a dependable recovery capability that limits downtime and data loss.
The comparison clarifies trade‑offs: local snapshots reduce downtime, while immutable and air‑gapped solutions provide stronger protection against coordinated attacks.
What Are Recovery Point and Time Objectives in Malware Incidents?
Recovery Point Objective (RPO) sets the maximum acceptable data loss measured backwards from an incident; Recovery Time Objective (RTO) sets the maximum tolerable outage before services must be restored. For SMEs, targets vary by service criticality: transactional systems often require RPOs in minutes and RTOs in hours, while internal documentation may tolerate longer windows. Setting realistic objectives requires a business‑impact analysis that maps services to customer and regulatory expectations, then designing backups and recovery playbooks to meet those targets. Regular testing validates that chosen RPOs and RTOs are achievable and highlights investment trade‑offs between backup frequency, storage costs and recovery automation.
- Example SME tiers: critical services — RPO minutes, RTO hours; non‑critical — RPO hours, RTO days.
- Testing approach: simulate ransomware recovery to measure actual RTO and refine objectives.
- Outcome: validated objectives inform procurement and response investments.
Defining and testing RPO/RTO ensures recovery expectations are realistic and resources focus on the systems that matter most.
Why Choose Stratlane for Cybersecurity Certification and Malware Protection?
Stratlane Certification Ltd. audits organisations for ISO standards including ISO 9001 , ISO 14001, ISO 27001 and ISO 42001. We position ourselves as an innovative Certification Body that combines AI tools with experienced industry auditors. Accredited certification gives organisations an objective framework to show customers, suppliers and regulators that information security and AI governance are managed systematically. Stratlane’s approach includes accredited certification, global reach with local audit teams, SME support programmes and clear guidance on standards and the audit process — all designed to help organisations translate ISO requirements into stronger anti‑malware controls and recovery capabilities.
How Does Stratlane’s Accredited ISO 27001 Certification Benefit UK Businesses?
Accredited ISO 27001 certification from Stratlane helps businesses turn security investment into demonstrable controls recognised by regulators and partners, improving supplier trust and competitive positioning. Certification validates that an ISMS governs asset management, access control, patching and incident response — all of which reduce malware exposure and speed recovery. For organisations wanting to reassure stakeholders, certification provides an independent assessment that security processes are implemented and continually improved. Stratlane combines accreditation, experienced auditors and practical guidance to support measurable improvements in malware resilience without prescribing a one‑size‑fits‑all technical stack.
What Support Does Stratlane Offer for SMEs Seeking Malware Protection?
Stratlane offers SME support programmes and local audit teams that reduce the friction of achieving accreditation by pairing practical guidance with tailored audit services. This includes clear advice on standards, help mapping business risks to Annex A controls and a straightforward pathway to accredited certification that strengthens cyber posture. For SMEs ready to act, the next step is to request a quote or book an audit to begin a structured ISMS implementation that integrates anti‑malware measures, backup strategies and AI governance where relevant. Stratlane’s model emphasises accessible certification and hands‑on support to help organisations translate standards into operational improvements.
- Request a quote or audit : start with a gap assessment to prioritise malware controls.
- Map risks to controls : align business‑critical assets to ISO requirements.
- Implement and test : deploy technical and organisational measures and validate them through exercises.
These steps make certification a practical route to stronger security and operational resilience, helping organisations manage malware risk with confidence.
Frequently Asked Questions
What steps can businesses take to enhance their malware detection capabilities?
Improve malware detection by adopting a layered security approach: deploy advanced endpoint protection, keep software patched, and centralise logging. A SIEM can aggregate alerts and help spot suspicious patterns. Regular vulnerability assessments and penetration tests identify weaknesses before attackers exploit them. Don’t forget people‑focused measures: train staff to recognise phishing and other social‑engineering tactics, since human error often enables infections.
How often should businesses conduct cybersecurity training for employees?
We recommend quarterly formal training backed by monthly micro‑learning to keep awareness high. Simulated phishing exercises every quarter help measure real‑world behaviour. Use the results to target retraining and continuously refine content so training stays relevant to evolving threats.
What role does incident response play in malware protection?
Incident response is central to malware protection: it defines how to detect, contain, eradicate and recover from incidents. A clear incident response plan enables fast action to limit damage, preserve evidence and restore services. Regular testing and updates ensure teams are prepared for real scenarios, reducing recovery time and limiting business impact.
How can businesses ensure their backups are secure against malware attacks?
Secure backups by using multiple copy types (local snapshots, offsite immutable backups and air‑gapped archives), encrypting data in transit and at rest, and strictly controlling access to backup systems. Regularly test restores to confirm backups are usable. These steps reduce the risk of simultaneous compromise during a malware event.
What are the benefits of obtaining ISO 27001 certification for malware protection?
ISO 27001 provides a structured ISMS to manage information security risks, including malware. Certification shows stakeholders that you follow a recognised framework for risk assessment, control implementation and continual improvement. It creates a clear roadmap for organising technical and operational protections and provides independent validation that security processes are in place and maintained.
How can businesses assess their current malware risk exposure?
Assess malware exposure through a comprehensive risk assessment: identify critical assets, catalogue vulnerabilities and estimate threat likelihood. Complement this with threat modelling, vulnerability scans, audits and penetration tests to reveal real‑world gaps. Use findings to prioritise controls and align them with ISO risk treatment plans.
Conclusion
Strong malware protection is essential for UK businesses to protect operations and data. Using frameworks such as ISO 27001 helps organisations manage risk methodically, reduce exposure and improve incident response. If you’re ready to strengthen resilience, request a quote or book an audit with Stratlane to begin a structured ISMS programme. Act now to reduce risk and limit the impact of future incidents.