Enhance Workplace Safety: ISO 45001 Drives OHS Compliance
ISO 45001 is the international standard for an Occupational Health and Safety Management System (OHSMS). It helps organisations reduce workplace risk, protect employee wellbeing and demonstrate alignment with UK regulatory expectations. This guide sets out what ISO 45001:2018 requires, how the PDCA cycle (Plan‑Do‑Check‑Act) supports continual improvement, and why ISO 45001 certification in the UK matters for suppliers and employers in 2024. You’ll find practical implementation steps, a clause‑by‑clause action map, audit readiness checklists and migration advice for organisations moving from OHSAS 18001. The guide also covers psychosocial risk management with reference to ISO 45003 and offers SME‑friendly pathways. Keywords covered include iso 45001, ohs certification, occupational health and safety management system, pdca cycle iso 45001, and iso 45001 audit to make this a useful resource for boards, H&S managers and procurement teams.
Research also highlights why structured preparation matters most in heavier industrial sectors.
ISO 45001 Certification Preparation Guidelines
This study highlights that occupational health and safety factors are central to running industrial businesses and to social sustainability. It examines preparation guidelines for ISO 45001 certification and develops those guidelines into a structural equation model.
The Guidelines for Preparation of Certified ISO 45001: The Occupational Health and Safety Management System, N Sawatenarakul, 2023
Beyond occupational health and safety, many organisations also pursue ISO 9001 certification to show commitment to quality management and to help ensure consistent product and service delivery.
What is ISO 45001 and Why is it Essential for UK Businesses?
ISO 45001 (ISO 45001:2018) sets out requirements for establishing, implementing and maintaining an OHSMS to prevent work‑related injury and ill health. The standard asks organisations to understand their context and risks, put effective controls in place, involve workers and show visible leadership commitment. When applied correctly, ISO 45001 delivers measurable reductions in incidents and improves workplace wellbeing. For UK businesses, the standard complements legal duties by providing a clear framework for meeting regulatory expectations and demonstrating due diligence. Increasingly, regulators and large buyers regard accredited certification as evidence of systematic OHS management and risk control, which reinforces the standard’s practical value.
Defining ISO 45001 and the Occupational Health and Safety Management System
ISO 45001:2018 describes an Occupational Health and Safety Management System as a structured approach to manage hazards, legal obligations and continual improvement for health and safety. An OHSMS typically includes policy and objectives, risk assessment and controls, competence and training, operational controls, monitoring, internal audit and management review — each element contributing to the whole. Organisations across construction, manufacturing, professional services and logistics use the standard to organise their health and safety programmes and to build worker participation into decision making. Getting scope, interested parties and leadership responsibilities right lays the groundwork for effective implementation, PDCA cycles and audit readiness.
Current UK Workplace Safety Landscape and Regulatory Compliance
Recent UK data underline the business case for ISO 45001: work‑related ill health and injuries continue to impose costs through lost working days and compensation, and regulators increasingly expect robust management systems as evidence of control. While certification is voluntary, ISO 45001 maps directly to legal duties enforced by the HSE and local authorities, helping organisations meet obligations to assess risk, provide training and keep records. Adopting an OHSMS reduces exposure to common non‑conformities and demonstrates proactive OHS compliance when engaging with enforcement bodies or major clients. That context explains why many organisations prioritise certification as part of wider risk and procurement strategies.
What Are the Key Benefits of ISO 45001 Certification for Companies?
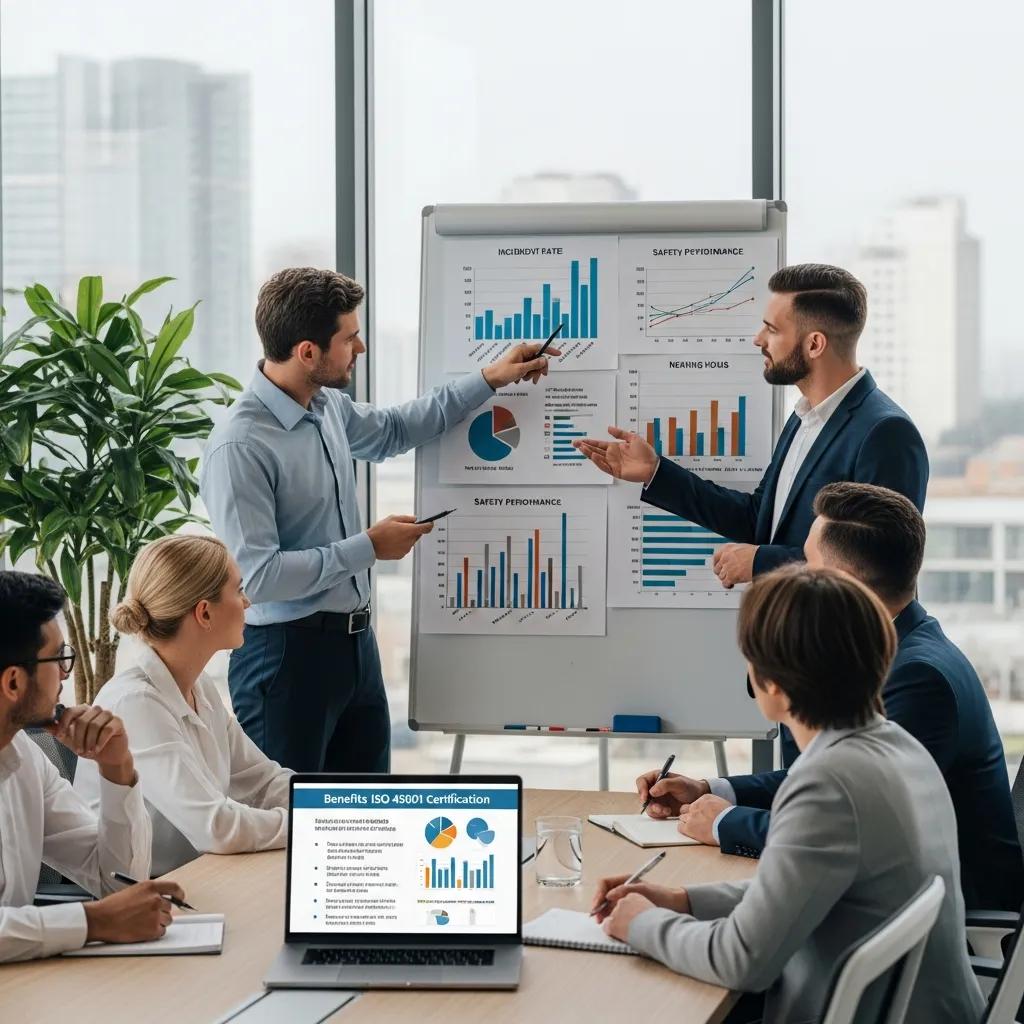
When implemented well, ISO 45001 delivers measurable gains across safety, cost control and market positioning. The standard helps organisations reduce risk through systematic assessment and controls, improves employee wellbeing by embedding participation and consultation, and strengthens commercial credibility when bidding for contracts that specify accredited OHS certification. Certification can also support better insurance discussions, increase operational resilience and improve supplier assurance — outcomes that matter to stakeholders and underwriters. Below is a concise summary of the main benefits companies typically realise from an effective OHSMS.
ISO 45001 delivers these core advantages:
- Better safety performance through structured risk assessment and preventative controls that reduce incidents and their costs.
- Stronger employee engagement by formalising worker participation, which increases reporting and speeds hazard correction.
- Closer regulatory alignment and documented evidence of OHS compliance that can lower enforcement risk and support legal due diligence.
- Competitive edge in tenders and supply chains where accredited certification is a requirement or differentiator.
Those benefits tie directly to operational savings and reputational gain, and they lead naturally to the practical question of how to implement the standard clause by clause.
Intro to measurable business outcomes table: below is a concise comparison of typical business impacts to help quantify expected outcomes after certification.
| Business Area | Potential Impact | Typical Outcome |
|---|---|---|
| Insurance | Reduced perceived risk | Possible premium negotiation or improved terms |
| Productivity | Fewer disruptions from incidents | Higher uptime and continuity |
| Employee Retention | Improved wellbeing and participation | Lower staff turnover and absenteeism |
| Tender Success | Proof of accredited OHSMS | Greater eligibility for public/private contracts |
Reducing Workplace Risks and Enhancing Employee Well-being
ISO 45001 reduces workplace risk by requiring documented hazard identification, risk assessment and proportionate controls that are monitored for effectiveness. Controls range from engineering solutions and safe systems of work to administrative procedures and competency programmes; each control is checked through internal audits and performance indicators to drive improvement. Worker participation mechanisms — consultation forums, straightforward reporting channels and involvement in investigations — support faster corrective action and better psychosocial outcomes. Tracking leading indicators such as near‑miss reporting and training completion gives early insight into system health and links directly to improved wellbeing.
Achieving Legal Compliance and Gaining Competitive Advantage
Certification provides evidence that legal obligations are managed systematically and supplies records for regulators and buyers who expect OHS compliance within supply chains. In procurement, ISO 45001 often appears in tender criteria and supplier assurance questionnaires, helping certified organisations meet buyer requirements and access larger contracts. Holding an accredited OHSMS also signals maturity to insurers and financial stakeholders and supports resilience by reducing incident‑related downtime. These commercial benefits, alongside better health outcomes, make certification a strategic asset for organisations seeking both compliance and market differentiation.
What Are the ISO 45001 Requirements and How to Implement Them?
ISO 45001 organises requirements across clauses 4–10: context, leadership, planning, support, operation, performance evaluation and improvement. The PDCA cycle offers the operational logic: plan by setting policy and objectives; do by applying controls; check through monitoring and audits; act by handling nonconformities and driving improvements. A practical clause mapping and clear steps translate the standard into day‑to‑day tasks for safety managers and leaders. The table below links clauses to concrete actions and implementation tips.
| Clause | Requirement | Practical Example / Implementation Tip |
|---|---|---|
| 4 — Context & Scope | Understand internal/external issues and interested parties | Run a context review and document scope with input from senior leaders |
| 5 — Leadership | Top management commitment and roles | Define responsibilities and embed H&S objectives into corporate plans |
| 6 — Planning | Hazard identification and risk control | Use a risk matrix, keep registers updated and include a legal requirements checklist |
| 7 — Support | Competence, awareness, communication | Provide role‑based training and record demonstrated competencies |
| 8 — Operation | Operational controls and contractors | Put safe work procedures in place and manage contractor arrangements |
| 9 — Performance Evaluation | Monitoring, internal audit, management review | Schedule surveillance and internal audits; track relevant KPIs |
| 10 — Improvement | Corrective action and continual improvement | Apply root‑cause analysis and use an action‑tracking system |
Intro to numbered implementation checklist: below is a practical, time‑aware sequence to follow when implementing an OHSMS.
- Conduct a gap analysis and context review to set scope and baseline risks.
- Draft policy and objectives, and assign leadership responsibilities with measurable KPIs.
- Document processes for hazard identification, operational controls and contractor management.
- Deliver role‑based competence and awareness training across the workforce.
- Run internal audits, close corrective actions and schedule management reviews to address gaps.
Overview of ISO 45001 Clauses and the Plan-Do-Check-Act Cycle
Clauses 4–10 create the management backbone: clause 4 sets context and scope; clause 5 secures leadership; clause 6 addresses planning; clause 7 covers support; clause 8 manages operations; clause 9 evaluates performance; clause 10 drives improvement. PDCA ties these together: planning defines objectives and controls, doing implements them, checking measures performance via monitoring and audit, and acting addresses nonconformities and opportunities. Simple relationships help clarify the flow: “Leadership → commits to → policy and resources”, “Risk assessment → identifies → controls”, “Internal audit → verifies → conformity and effectiveness”. Applying PDCA across clauses keeps OHSMS progress steady and auditable.
The Plan‑Do‑Check‑Act (PDCA) cycle is widely accepted as the core mechanism for maintaining effective management systems, including occupational health and safety.
PDCA Cycle in ISO 45001 Management Systems
Research confirms PDCA is the cycle to maintain in integrated management systems, helping organisations structure key requirements such as organisation and stakeholder engagement for continual improvement.
An alternative integrated occupational health, safety and environmental management system for small and medium-sized enterprises (SMEs) in Thailand, 2019
Steps for Effective Implementation of an Occupational Health and Safety Management System
Effective implementation blends governance, operational change and verification with clear ownership and timelines. Start with a readiness pack (documented scope, legal register, risk register, training matrix) and run a gap analysis to prioritise actions. Develop documentation and proportionate operational controls for identified hazards, then roll out training and communications. Follow with internal audits and management reviews to test effectiveness and drive corrective actions. Common pitfalls include weak leadership engagement and limited worker consultation; addressing those early improves your chances of successful certification and lasting performance.
How Does the ISO 45001 Audit Process Work with Stratlane Certification Ltd.?
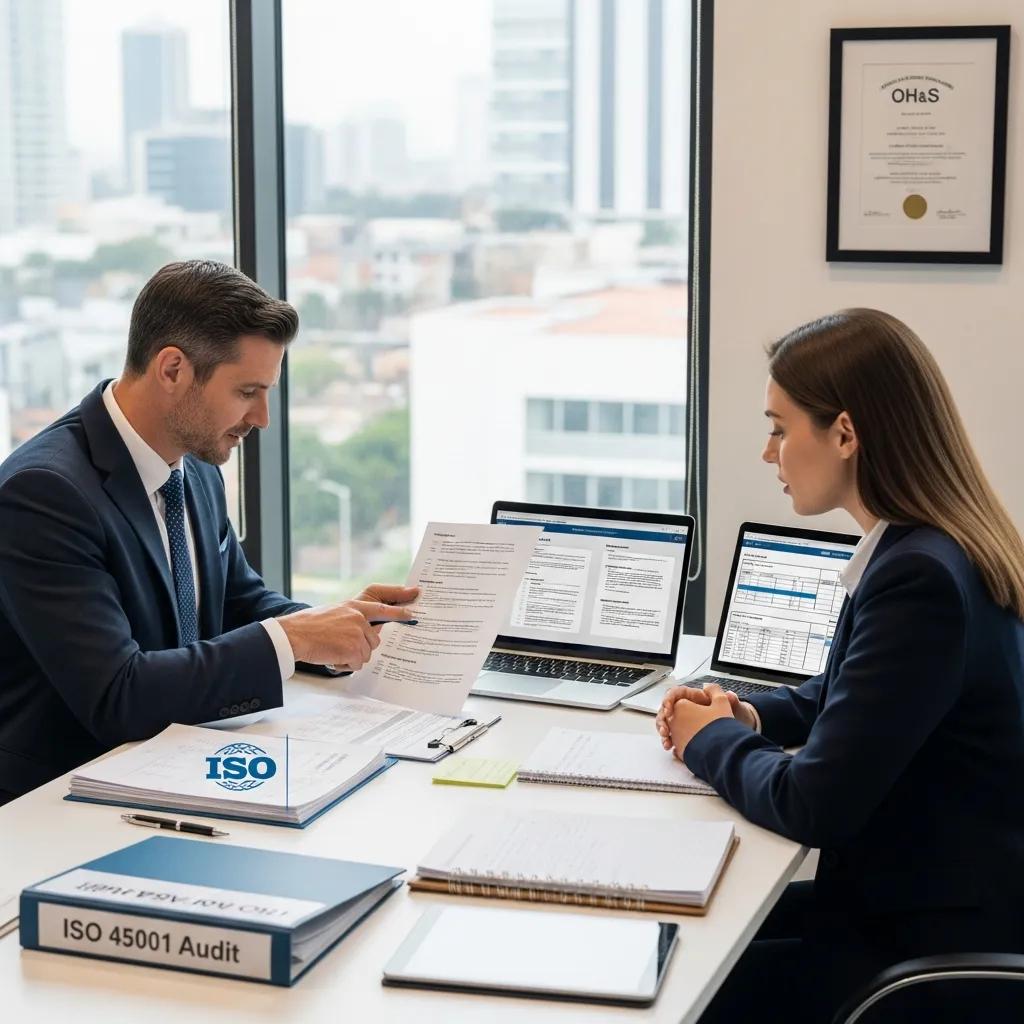
An ISO 45001 audit typically follows stages: readiness/gap analysis, Stage 1 documentation review, Stage 2 on‑site or remote system evaluation, and ongoing surveillance audits to maintain certification. Assessors look for objective evidence that the OHSMS meets the clauses, that workers are engaged and that continual improvement is in place. Preparing clear records, closing internal audit findings and showing leadership involvement are key client responsibilities before external assessment. The table below summarises audit stages, expected deliverables and typical timings to help teams plan resources.
| Audit Stage | Focus / Deliverable | Typical Duration / Client Action |
|---|---|---|
| Gap Analysis / Readiness | Identify compliance and implementation gaps | 1–2 weeks; client provides documentation and access |
| Stage 1 — Documentation Review | Verify scope, policy, legal register and documented controls | 1–2 days remote; client submits documents in advance |
| Stage 2 — System Evaluation | On‑site or remote verification of implementation and worker engagement | 2–5 days depending on scope; client arranges interviews and records |
| Surveillance Audits | Periodic checks to ensure continued conformity | Annually or biannually; client maintains records and improvements |
| Recertification | Full reassessment at cycle end | Every 3 years; client demonstrates ongoing improvement |
Introductory numbered list of audit preparation tasks: preparing for an ISO 45001 audit requires focused, document‑driven activity.
- Finalise scope and confirm the legal register is up to date.
- Complete internal audits and record corrective actions.
- Gather evidence of worker consultation and training records.
- Schedule availability of key personnel for Stage 2 interviews.
Stratlane Certification Ltd. combines AI‑enabled tools with an auditor‑led approach to support readiness analysis and accredited certification across the UK, Ireland and mainland Europe. Their methodology uses AI to speed up document review and highlight gaps, while experienced auditors apply sector judgement to validate implementation and guide corrective actions. For organisations seeking an accredited partner with digital readiness capabilities, Stratlane offers services designed to align practical evidence with ISO 45001 audit expectations across different operational scales.
In addition to health and safety, many organisations prioritise information security. It is common to pursue ISO 27001 certification to establish an Information Security Management System that protects sensitive data and helps ensure business continuity.
Stages of ISO 45001 Audits: Gap Analysis, Internal and External Audits
A gap analysis sets the baseline by comparing current practice with ISO 45001 requirements and produces a prioritised remediation plan that guides implementation and internal audits. Internal audits check that procedures are followed and that corrective actions are effective — feeding into management review and external readiness. Stage 1 confirms the system design exists; Stage 2 verifies implementation and worker participation in practice. Surveillance audits then ensure ongoing conformity. Typical non‑conformities include incomplete risk registers, insufficient monitoring or gaps in training; tackling these early reduces delays at assessment.
Role of AI-Driven Tools and Experienced Auditors in Certification
AI tools can accelerate readiness by analysing documents, flagging gaps and surfacing trends in incidents and training coverage, which makes internal audits more efficient and helps prioritise risk. Experienced auditors add sector knowledge and judgement to interpret context, assess controls and validate worker engagement — a combination that strengthens audit outcomes. Tools can identify entities such as “policy”, “risk assessment” and “competence” and link them to evidence, while auditors translate those links into practical findings. Together, technology and human expertise create a balanced route to robust ISO 45001 certification.
How to Transition from OHSAS 18001 to ISO 45001 Successfully?
Moving from OHSAS 18001 to ISO 45001 means shifting from a mainly procedural approach to risk‑based thinking with greater emphasis on leadership and worker participation. Begin with a gap analysis that focuses on context, leadership requirements and risk‑based planning, then update policies, processes and documentation to match the ISO 45001 clause structure. A clear migration checklist and timeline helps teams sequence tasks and prepare for re‑assessment. Below is a direct comparison followed by a short migration checklist to show the practical differences and required actions.
Transitioning from OHSAS 18001 to ISO 45001 is a substantial change that organisations often coordinate with other integrated standards such as ISO 9001 and ISO 14001.
ISO 45001 Migration from OHSAS 18001
Guidance on migration emphasises the benefits of aligning BS OHSAS 18001:2007 with international standards such as ISO 9001, ISO 14001 and ISO 45001 to support integrated management systems and smoother transitions.
Considerations on Migration from BS OHSAS 18001: 2007 to ISO 45001: 2018 in the Context of Integrated Management System, DC Darabont, 2007
| Aspect | OHSAS 18001 | ISO 45001 |
|---|---|---|
| Approach | Often procedural and control-focused | Risk-based with strategic context and leadership emphasis |
| Leadership | Management commitment expected | Explicit leadership and accountability requirements |
| Worker Participation | Consultation recommended | Active worker participation integral to design and implementation |
| Structure | Less aligned with other ISO standards | High-level structure aligned with Annex SL for integration |
Transition checklist (yes/no style with actions):
- Have you completed a gap analysis against ISO 45001 clauses? — If no, schedule one immediately.
- Have you updated policy and leadership responsibilities to reflect ISO 45001? — If no, revise governance documents.
- Have you documented worker participation mechanisms and evidence? — If no, implement consultation and record outcomes.
- Have you aligned risk assessment methods to risk‑based thinking? — If no, update risk registers and controls.
Stratlane Certification Ltd. can support migration with targeted gap analyses and tailored audit plans that mirror the ISO 45001 clause structure and practical needs of organisations moving from OHSAS 18001. Their use of AI for readiness analysis combined with experienced auditors helps focus remediation and streamline the migration timeline while keeping attention on worker participation and leadership responsibilities. Organisations seeking external coordination for migration and certification can use Stratlane’s services to help reduce surprises at Stage 2.
Differences Between OHSAS 18001 and ISO 45001 Standards
The move from OHSAS 18001 to ISO 45001 centres on proactive risk management, clearer leadership accountability and formalised worker participation — reflecting modern expectations for risk governance. ISO 45001 applies risk‑based thinking across planning and operations and requires organisations to consider context and interested parties, which was less explicit under OHSAS 18001. Practically, this means more documented evidence of leadership commitment, defined processes for worker involvement and better alignment with other management systems, supporting integrated compliance and reporting. Recognising these differences explains why migration needs both technical updates and cultural change.
Stratlane’s Support for a Smooth Migration Process
Stratlane Certification Ltd. provides migration‑focused services including targeted gap analysis, readiness reporting and tailored audit schedules. Their AI tools highlight priority remediation and experienced auditors validate progress. The approach emphasises practical deliverables — updated documentation, evidence of worker participation and closure of key non‑conformities — to shorten time to certification while aligning with accredited standards across jurisdictions. Organisations using structured migration support usually experience clearer audit pathways and fewer surprises during Stage 2.
How Does ISO 45001 Address Psychosocial Risks and Support SMEs?
ISO 45001 recognises psychosocial risks as part of the hazard spectrum and, together with ISO 45003 guidance, offers a framework for assessing and managing factors such as workload, organisational change and workplace culture that affect mental health. The standard requires psychosocial hazards to be included in risk assessments, controlled proportionately and reviewed for effectiveness through employee feedback and performance indicators. SMEs can adopt scaled controls — simple risk registers, regular check‑ins and low‑cost training — that meet the standard without excessive administrative burden. Below is a practical SME approach to make psychosocial risk management workable and effective.
Managing Psychosocial Risks with ISO 45003 Guidance
ISO 45003 complements ISO 45001 by explaining how to identify and manage psychosocial hazards. It provides prompts and control ideas such as workload management, clearer role definitions and supportive leadership practices. Practical steps include staff surveys for stress indicators, mapping high‑risk tasks and applying measures like adjusted workloads, flexible working and access to wellbeing resources. Measure effectiveness through absence trends, engagement scores and incident reports so management review can drive continual improvement. Applying ISO 45003 helps treat psychosocial risks with the same rigour as physical hazards.
Tailored ISO 45001 Solutions for Small and Medium-sized Enterprises
SMEs benefit from a simplified six‑step pathway that scales ISO 45001 into practical actions: define scope, keep a concise risk register (including psychosocial items), apply proportionate controls, deliver basic training, perform short internal checks and hold a management review. This approach minimises paperwork while meeting core requirements and provides a cost‑effective route to certification readiness. Stratlane adapts audit scope for smaller organisations by focusing on critical controls and pragmatic evidence, enabling SMEs to pursue accredited certification without unnecessary bureaucracy. For many smaller businesses, this scaled approach makes ISO 45001 achievable and valuable.
Introductory list: a simplified SME pathway for ISO 45001 implementation.
- Define scope and key activities to keep complexity manageable.
- Create a concise risk register that includes psychosocial hazards.
- Implement proportionate controls and clear procedures.
- Provide focused training for managers and affected staff.
- Conduct short internal audits and record improvements.
- Hold a management review to close the PDCA loop.
For organisations ready to proceed, Stratlane Certification Ltd. positions itself as an AI‑enabled, auditor‑led partner that adapts audit scope to SME needs and supports certification accepted across multiple jurisdictions.
As technology evolves, responsible AI governance becomes increasingly important. Stratlane also supports organisations pursuing ISO 42001 certification , an emerging framework for AI management systems that helps ensure ethical and effective AI deployment.
Stratlane Certification Ltd., an AI‑enabled certification body based in London, offers accredited ISO audits and certification for ISO 45001 and related standards. They combine digital readiness tools with experienced auditors to support organisations through gap analysis, Stage 1 and Stage 2 audits and surveillance cycles. Their accreditation is accepted in over 30 countries and they deliver audits across the UK, Ireland and mainland Europe while supporting clients globally. Organisations seeking an accredited partner with a technology‑enhanced approach can request a quote or book an audit with Stratlane Certification Ltd. to start their certification journey.
Frequently Asked Questions
What is the difference between ISO 45001 and OHSAS 18001?
Both standards focus on occupational health and safety, but ISO 45001 adopts a more proactive, risk‑based approach. It requires stronger leadership engagement and explicit worker participation and asks organisations to consider their context and interested parties. ISO 45001’s high‑level structure also makes integration with other ISO standards easier. Overall, ISO 45001 provides a more comprehensive framework for modern risk governance.
How can small and medium-sized enterprises (SMEs) implement ISO 45001 effectively?
SMEs can follow a simplified six‑step pathway: define scope, keep a short risk register, apply proportionate controls, deliver focused training, run short internal audits and hold management reviews. This keeps documentation light while meeting core requirements. Tailor the standard to your operations and prioritise the most significant risks to make certification achievable without heavy bureaucracy.
What role does employee participation play in ISO 45001?
Employee participation is central to ISO 45001. The standard expects workers to be involved in identifying hazards, assessing risks and developing controls. Engagement improves hazard reporting, speeds corrective actions and helps build a stronger safety culture. Valuing employee input leads to better system effectiveness and healthier workplaces.
What are the key steps in the ISO 45001 audit process?
The audit process usually includes a gap analysis, a Stage 1 documentation review and a Stage 2 evaluation of implementation and worker engagement, followed by surveillance audits to maintain certification. Preparing clear records and demonstrating leadership involvement are vital for a smooth assessment. This structured approach supports ongoing improvement and certification maintenance.
How does ISO 45001 address psychosocial risks in the workplace?
ISO 45001 requires organisations to assess psychosocial hazards — for example workload, culture and change — and to apply proportionate controls. Using ISO 45003 guidance helps identify specific risks and practical controls such as workload adjustments, clearer roles and wellbeing resources. Measuring outcomes through absence, engagement and incident data informs improvement and ensures psychosocial issues are managed like any other hazard.
What benefits can organizations expect from ISO 45001 certification?
Certified organisations typically see better safety performance, stronger employee engagement and clearer regulatory compliance. Certification demonstrates systematic risk management, which can reduce incidents and associated costs and improve access to tenders where accredited certification is required. Overall, ISO 45001 supports resilience and enhances an organisation’s standing with stakeholders and clients.
Conclusion
ISO 45001 certification delivers real benefits: safer workplaces, stronger employee engagement and clearer regulatory alignment. The standard gives organisations a structured, auditable framework to manage risk and demonstrate due diligence, which also supports commercial credibility. By making occupational health and safety a strategic priority, businesses can foster a culture of wellbeing that benefits employees and stakeholders alike. To start your certification journey, explore Stratlane Certification Ltd.’s tailored services and get a quote today.